Cloud & DevOps · Open-source build
Signed software supply chain with policy gates
Every image is scanned, signed and attested in CI, and the cluster refuses anything that is not. Security as a gate, not a slide.
What it is
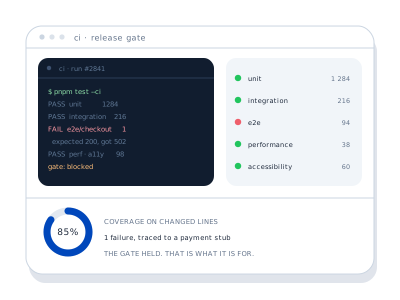
Cosign signs each image with a keyless Sigstore identity tied to the CI workflow. An SBOM and a vulnerability report ride along as attestations. Kyverno policies in the cluster verify the signature and reject unsigned or critically vulnerable images at admission, so the rule is enforced where it matters.
What the build consists of
- 01Trivy scans for OS and library vulnerabilities with a policy on severity
- 02Cosign keyless signing bound to the GitHub Actions OIDC identity
- 03SBOM generation with Syft attached as an in-toto attestation
- 04Kyverno ClusterPolicies: verify signature, require resource limits, block latest tags
- 05Policy reports surfaced in Grafana next to workload health
- 06Break-glass procedure documented and tested
What you see in a demo
Pushing an unsigned image and watching the cluster reject it with a readable reason. Auditors and security leads recognise the pattern at once.